Java
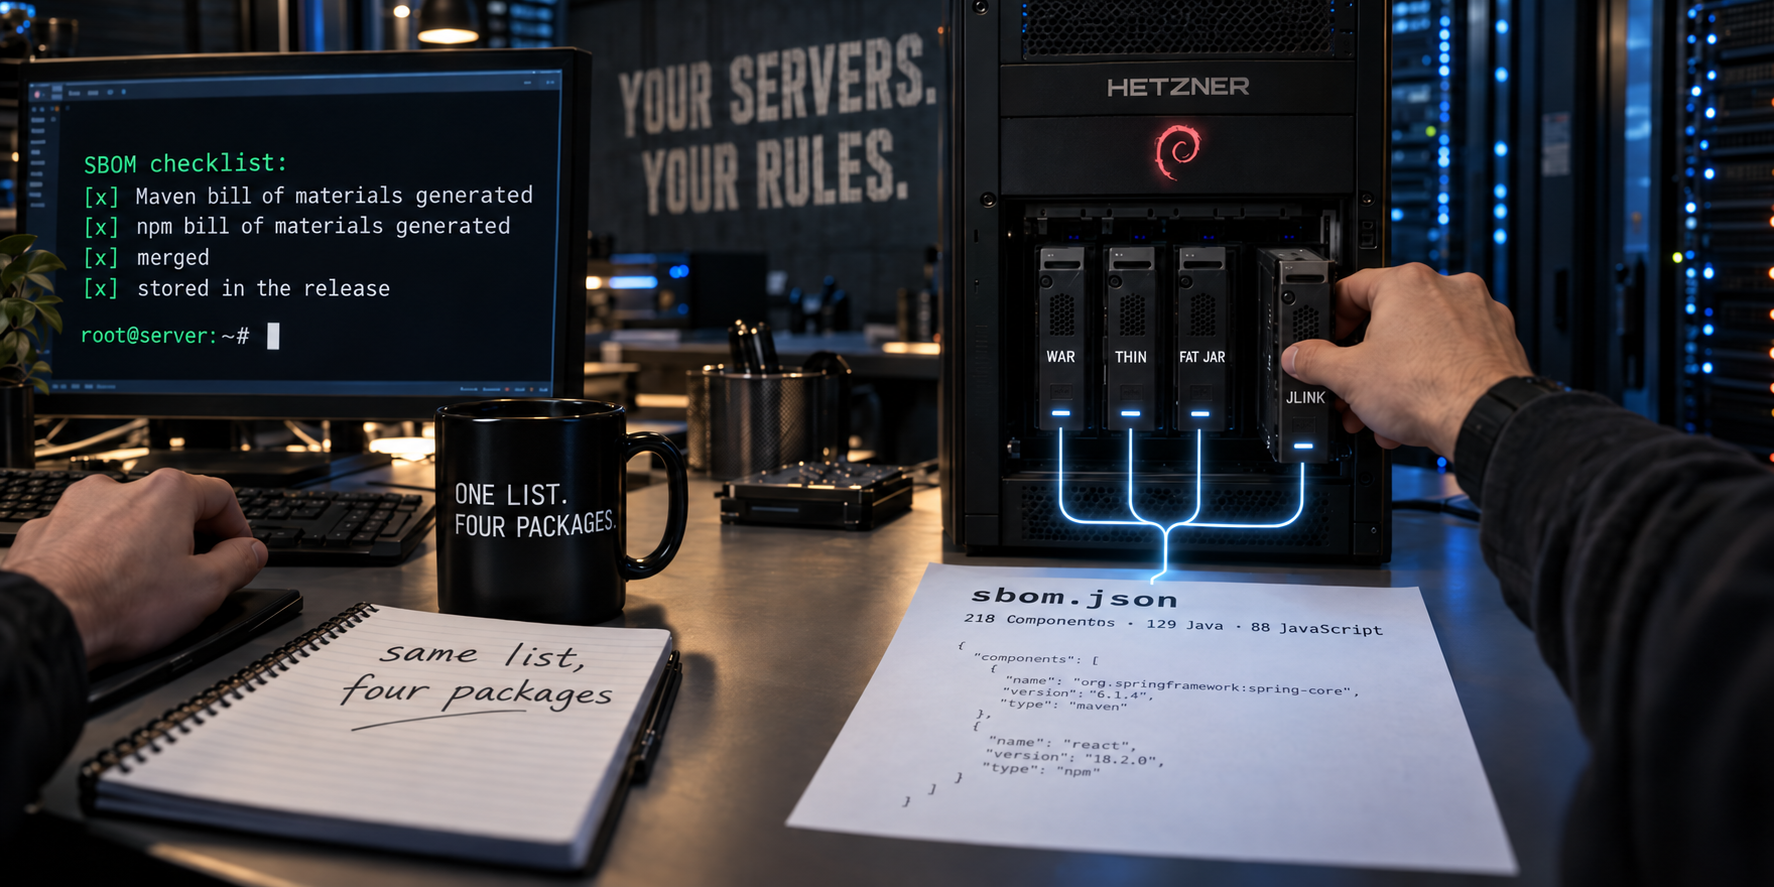
Four Delivery Formats, One SBOM
First of two articles on software bills of materials. One application, four delivery formats, one server — and the question of what the …
First of two articles on software bills of materials. One application, four delivery formats, one server — and the question of what the …
Foundation article of the series Vaadin – Deployment on Hetzner. It produces the server on which the following parts put a Vaadin …
Second of two articles about software bills of materials. The inventory is in place — what it can answer, and what it cannot: …
Part I – The incident A screenplay that isn’t one A program leaves the sealed room in which it was meant to be examined, gains access …
Basis: Vaadin 25.2 release post and the official security documentation at vaadin.com/docs/latest/flow/security. Table of Contents …
Password security is an often underestimated but critical topic in software development. Databases containing millions of user logins are …
A URL shortener seems harmless – but if implemented incorrectly, it opens the door to phishing, enumeration, and data leakage. In this first …
1. Getting started – trust in everyday internet life Anyone who enters a web address like “www.example.de” into the browser expects a …
The Java Cryptography Architecture (JCA) is an essential framework within the Java platform that provides developers with a flexible and …
Cache poisoning on Maven Caches is a specific attack that targets how Maven Caches manages packages and dependencies in a software …
Learn how inadequate control over error reporting leads to security vulnerabilities and how to prevent them in Java applications. Safely …
Building on the discussion of “CWE-377: Insecure Temporary File”, it’s essential to delve deeper into one of the most insidious …